Secure gateway architecture
A secure gateway connects a specific functional domain — workstations, appliance, secrets, identity — to the Reemo platform core, without ever exposing the API directly. Each gateway talks to the core over mTLS (mutual TLS) on a dedicated PKI.
This model compartmentalizes trust: each gateway holds its own cryptographic identity, and a compromised domain does not open access to the others.
Principle
A secure gateway enforces three mechanisms:
Mutual authentication (mTLS): the gateway and the core each present a certificate, and each verifies the other’s. A client without a valid certificate is rejected.
Dedicated PKI: the gateway’s certificates are issued by a certification authority specific to its domain, separate from the shared internal PKI.
Per-gateway identity: each gateway has its own certificate, which lets it be isolated, revoked, or renewed independently.
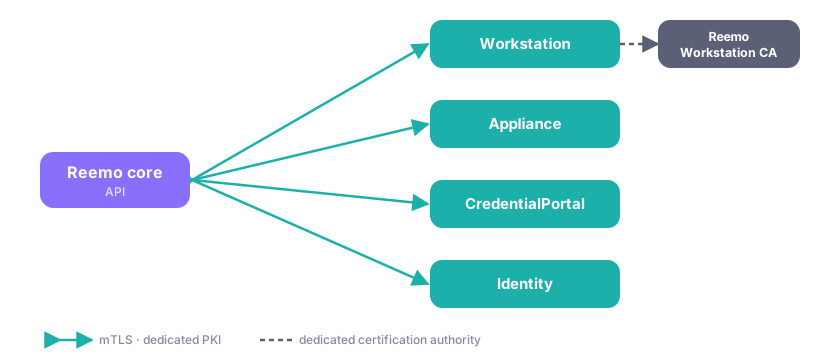
Secure gateways talk to the core over mTLS on a dedicated PKI.
The gateways
Workstation: connects workstations (Reemo Desktop agents) to the core. It relies on a dedicated PKI, the Reemo Workstation CA, separate from the internal PKI.
Appliance: connects an appliance-type container provider, through the applianceportal gateway.
CredentialPortal: exposes the credential portal in front of the CredentialAPI and its vault.
Identity: handles authentication and identity federation, through the identityportal gateway.
Each one is deployed only if its domain is enabled in the instance.
mTLS with a dedicated PKI
The core trusts only the gateways whose certificate is issued by the right authority and still valid. Conversely, the gateway verifies that it is indeed the Reemo core answering. This verification is bidirectional and replayed on every connection.
Combined with distinct PKIs per domain, this model reduces the attack surface: a gateway cannot impersonate another domain, and the compromise of one domain stays contained.
See also
Secure Gateways — Create and configure a secure gateway in your instance.
See also
SSL Certificates — The certificate and PKI concept that secure gateways build on.